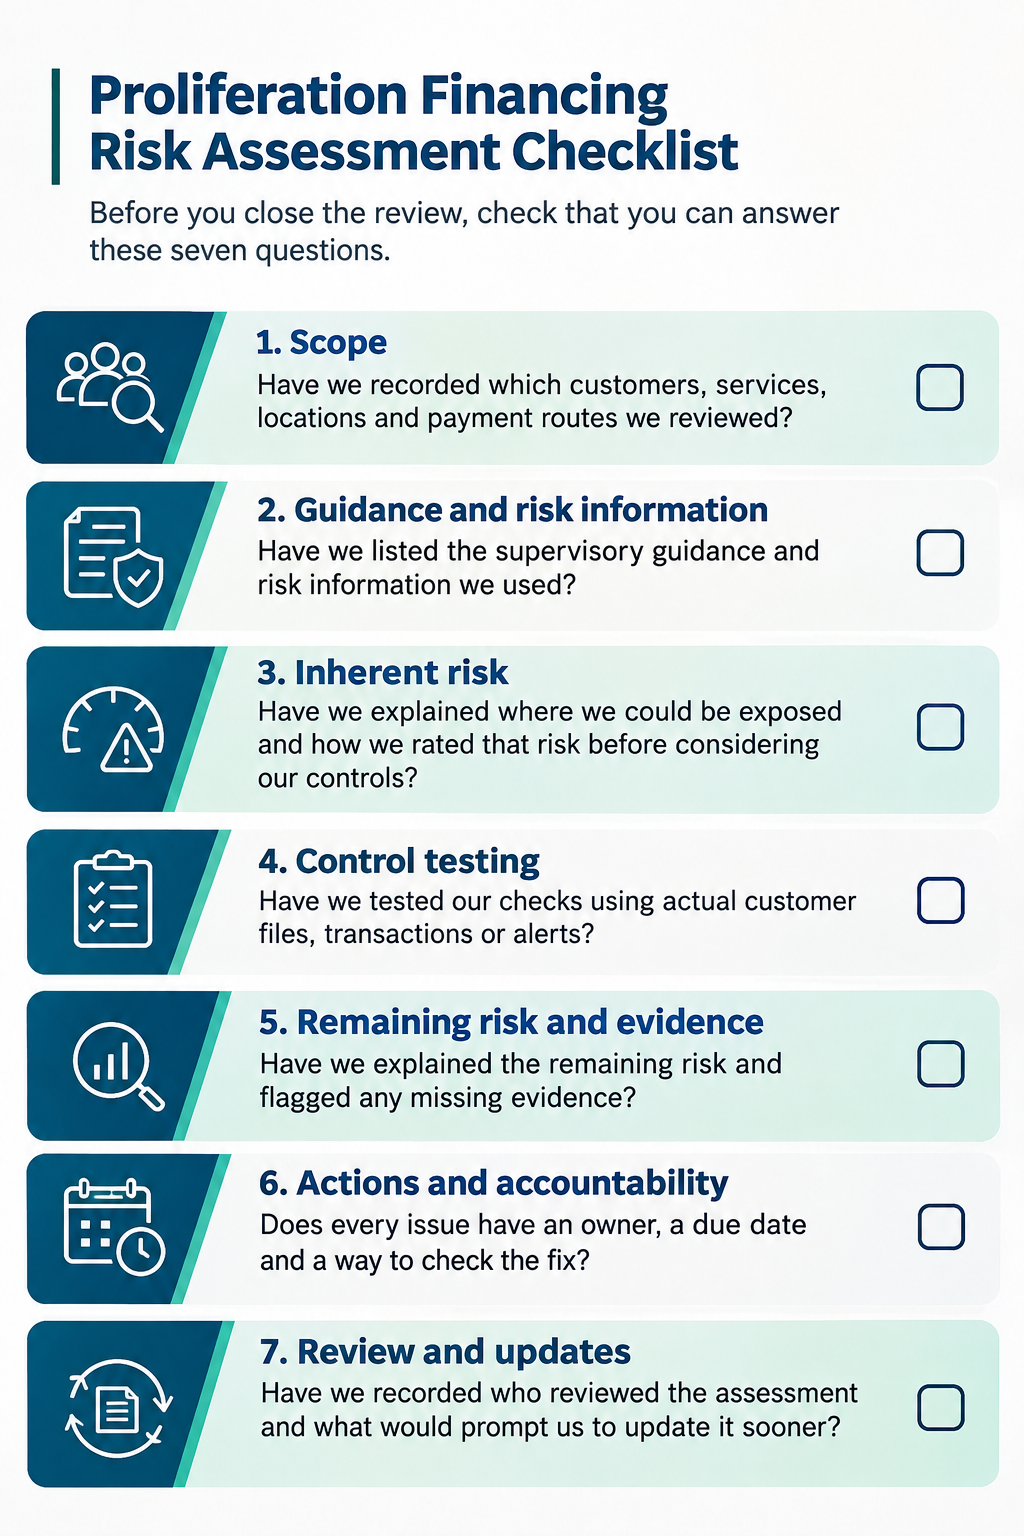
A customer passes sanctions screening when you onboard them. Three months later, a different company starts paying their invoices. Would anyone on your team notice? And if they did, would they know what to check?
That’s the kind of gap a proliferation financing risk assessment can uncover. It helps you see where your business could be exposed, whether your checks work in practice and what to fix first. If you’re new to the topic, start with our guide to proliferation financing, examples and red flags.
1. Decide What Your Assessment Will Cover
Start with how your business works. Who are your customers? What services do they use? How do you verify who you’re dealing with, and how does money move? Include agents, introducers and other intermediaries if they play a part.
The areas you review will depend on what you do. A trade finance team might look at goods descriptions, shipping routes and payment instructions. A company formation provider might examine how staff check who ultimately owns a client with several layers of ownership.
In the UAE, use the rules and supervisory guidance that apply to your sector. The Central Bank’s guidance covers the financial institutions it supervises. Designated non-financial businesses and professions (DNFBPs) should check their own supervisor’s guidance. Under FATF Recommendation 1, the assessment focuses on how proliferation-related targeted financial sanctions could be breached, missed or evaded. Applicable sanctions obligations still apply when your assessment rates the risk as low.
2. Identify Your Proliferation Financing Risk Factors
Look at where you could be exposed before you take your existing checks into account. That’s your inherent risk. For each area below, write down one situation that could happen in your business and pull the records that help you judge how likely or serious it is.
| Risk factor | What to ask | What to look at |
| Customers and ownership | Can we tell who ultimately owns or controls the companies we deal with? | Ownership charts, registry records and files with unanswered ownership questions |
| Products, services and transactions | Could our services be used to pay for sensitive goods or move money through a third party whose role is unclear? | Payment instructions, transaction records and trade documents where available |
| Countries and routes | Do we know where the payment or shipment is going and why it’s taking that route? | Counterparty locations, payment routes and shipping records where relevant |
| How customers come to us | What do we verify when a customer comes through an introducer or signs up remotely? | Onboarding files, verification records and any exceptions staff approved |
| Systems and procedures | Would anyone notice if the payer or another important detail changed? | Change logs, screening settings and records of who reviewed alerts |
An unusual payment route or a complex ownership structure gives you a reason to ask more questions. Write down what you could verify, what’s still unclear and how that affects your risk rating.
3. Test Your Counter-Proliferation Financing Controls
Pull a sample of customer files, changes to payment instructions and closed alerts. Follow each case from the initial check to the final decision. If your procedure says staff should review a new payer, look for a case where the payer changed and see what staff actually did.
- Ownership checks. Can you see who ultimately owns or controls the customer and which documents support that finding?
- Sanctions screening. Can you tell who was screened, when they were screened and how any potential matches were handled?
- Changes after onboarding. What did staff do when a payer, owner or destination changed?
- Escalation. Did the issue reach the right person? Does the file show who made the decision and why?
- Record keeping. Could someone who wasn’t involved follow the decision from the records alone?
If you can’t find evidence that a check took place, record that. It gives you a specific gap to follow up on.
4. Rate What’s Left and Decide What to Fix
Residual risk is the risk that remains after you account for the controls you’ve tested. Use your organisation’s rating method and write a short explanation for each rating. Flag where evidence was missing or a control still needs testing.
Example of a New Third-Party Payer
A UAE business checks its customers and their owners at onboarding. During a file review, the team finds that the payment process lets a different company pay an invoice without flagging the change for review.
The team records the gap and explains why it raises the remaining risk. The payments lead adds a step to flag new payers for review. Compliance then checks a sample of later cases to see whether staff recorded the payer’s relationship to the customer, carried out the relevant checks and documented the decision.
Give every fix an owner, a deadline and a way to check that it works. Review the assessment on your usual schedule and sooner if something changes, such as entering a new market, adding a payment channel or finding the same screening gap in several files.

Need Help Reviewing Your Exposure?
If you’re unsure where to start, Vertex Compliance can help you review your exposure across customers, transactions and markets and identify which checks need more attention. Learn more about our proliferation financing risk assessment service.
Frequently Asked Questions
1. Can we include proliferation financing in our existing AML risk assessment?
Yes, if your supervisor’s guidance allows it. Give proliferation financing a clear section or labelled entries so a reviewer can follow the risks you identified, the checks you tested and the actions you agreed on. See the FATF guidance on risk assessment and mitigation.
2. Could we be exposed if we never handle sensitive goods?
Yes. Think about what your services allow others to do. A payment provider may process a transfer through an intermediary whose role is unclear. A company formation provider may encounter a structure that makes it difficult to verify who is really in control. See the CBUAE guidance on proliferation financing risk factors.
3. Does a clean sanctions screening result mean the risk is low?
A clean result means the information you screened returned no match at the time. Check whose details went into that search. If you screened the customer but still haven’t verified who owns it or who is paying on its behalf, you have an open question to follow up on.
4. How often should we update the assessment?
Follow the review schedule that applies to your business and revisit the assessment sooner if your exposure changes. For example, if you start accepting customers through introducers, review how your team verifies those customers and what information it relies on. Record what prompted the update and which ratings or controls changed.
5. What evidence should we keep to support our risk ratings?
Keep enough for someone else to understand how you reached each rating. That could include the files you sampled, screening results, notes on exceptions and a short explanation of your decision. If you fixed a gap, keep the follow-up test results so the next reviewer can see whether the fix worked.
About the Author

Sridhar Rajam
Author details will be updated soon.