Call us today +971 - 56411 3575 or +971 - 58914 9282 | Email: info@vertexcompliance.com

Risk Assessments

Know where your business is exposed, which controls are working, and what needs attention first.

Request a Risk Assessment

    About Our Risk Assessment Services

    A risk assessment should give you more than a score on a spreadsheet. It should explain where risk enters your business, how your current controls respond, and what you need to do next.

    Vertex Compliance reviews the parts of your business that shape your exposure: your customers, products, services, transactions, delivery channels and the countries you deal with. We then look at the controls you have in place and the evidence that shows whether they work in practice.

    The result is a documented assessment your team can use to make decisions, set priorities and explain its approach to management or a regulator.
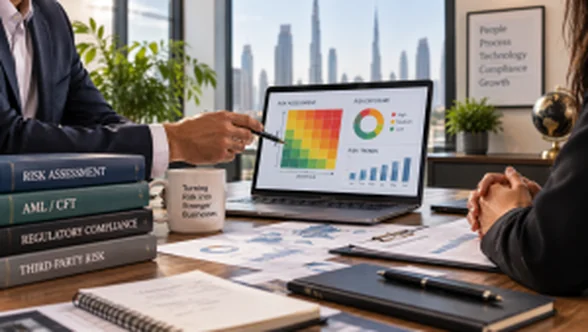
    Risk assessment

    What Our Risk Assessment Service Covers

    We look at where your financial crime risks are, how your controls hold up, and what needs attention.

    1. Enterprise-Wide Risk Assessment

    We start with how your business operates: the products you offer, the customers you serve, the markets you enter and the channels you use. Each can change the risks you face. We bring those factors together to build a clear view of risk across the business. We then review the controls you rely on and consider what risk remains after those controls are taken into account. The result helps your team see where exposure is greatest and where more attention may be needed.

    2. Financial Crime Risk Assessment

    Financial crime risk depends on what your business does and how money moves through it. We examine where you may be exposed to money laundering, terrorist financing, sanctions breaches, fraud and other relevant threats. That includes looking at your products, payment flows, customers and the places where you operate. We also consider the controls in place to manage those risks and identify gaps that need attention. This gives your team a clearer basis for deciding where to focus its compliance work.

    3. Customer Risk Assessment

    Not every customer presents the same level of risk. We review how you assess customers at onboarding and how those ratings are kept up to date as relationships change. This includes the factors used to assign a rating, when enhanced due diligence is required and what triggers a further review. We look at whether the approach reflects your customer base and can be applied consistently by your team. The aim is to make risk ratings easier to explain and more useful when deciding what action to take.

    Our Approach

    We keep our assessment focused, practical and relevant to your business.

    1
    Understand Your Business

    We review the information available and identify the risks relevant to your business. We consider both the likelihood of an issue and its potential impact, using a method that can be explained and applied consistently.

    2
    Identify and assess the risks

    We review the information available and identify the risks relevant to your business. We consider both the likelihood of an issue and its potential impact, using a method that can be explained and applied consistently.

    3
    Review existing controls

    We examine the policies, processes, systems and oversight used to manage those risks. Where needed, we speak with the people responsible for carrying out the controls.

    4
    Set out the findings

    We document the risks, the controls considered and the areas that need work. You receive practical recommendations, with the most pressing actions clearly identified.

    Who Our Risk Assessment Services Are For

    Banks and other financial institutions
    Designated Non-Financial Businesses and Professions (DNFBPs)
    Virtual asset service providers
    Fintech, payments and remittance businesses

    Ideal for financial institutions and businesses that need to understand their financial crime risks and strengthen the controls around them.

    Why Choose Vertex Compliance?

    Built Around Your Business

    We use your actual products, customers, channels and markets as the starting point.

    Clear, Explainable Risk Ratings

    A risk rating should make sense to the people using it. We document the information behind each conclusion so your team can explain how the assessment was reached.

    Attention to the Controls You Rely On

    A policy can describe a control well, but what matters is how it works day to day. We look at whether your controls address the risks they are meant to manage.

    Clear Priorities for Action

    Not every issue needs the same response. We identify what needs prompt attention and what can be improved over time, so your team has a practical place to start.

    Meet the Experts

    Sarah Khan
    Vasantha Madan Mohan

    Managing Director
    Sarah Khan
    Sridhar Rajam

    Associate Partner

    Sarah Khan
    Arjun Mohan

    Director – Sales & Marketing
    Frequently Asked Questions

    An enterprise-wide assessment looks at risk across the business, including its products, customers, channels and geographic exposure. A customer risk assessment focuses on how individual customers are rated and reviewed.
    No. We can help develop an initial assessment or review one you already use. The work will differ depending on what documentation, data and controls are available.
    That depends on the rules that apply to your business and how quickly its risk profile changes. A new product, market, customer segment or significant control issue may call for a review before the next scheduled update.
    Usually, we need information about your business activities, customers, products, locations, transaction patterns and existing controls. We confirm the specific request once the scope is agreed.
    Yes. The findings should show where action is needed and give your team a practical basis for planning that work.
    Yes. Vertex Compliance offers focused assessments for areas such as sanctions, fraud, payments and customer risk, as well as broader enterprise-wide assessments.