Call us today +971 - 56411 3575 or +971 - 58914 9282 | Email: info@vertexcompliance.com

AML/CFT Gap Assessment

Know where your business is exposed and which AML controls need attention.

Request a Consultation

    About Our Business Risk Assessment Services

    Your last risk assessment may have made sense when it was completed. Since then, you may have added a service, started accepting customers from another market, or seen a rise in overseas payments. The question is whether your AML controls still suit the business.

    At Vertex Compliance, we help UAE financial institutions, exchange houses, and designated non-financial businesses and professions (DNFBPs) review their exposure to money laundering and terrorist financing. We examine the business you operate today, using your records and conversations with the people handling the work.

    The assessment gives you a basis for making decisions. You can see where existing checks are sufficient, where weaknesses need attention, and which findings should lead to changes in your AML policies, procedures, or resources.
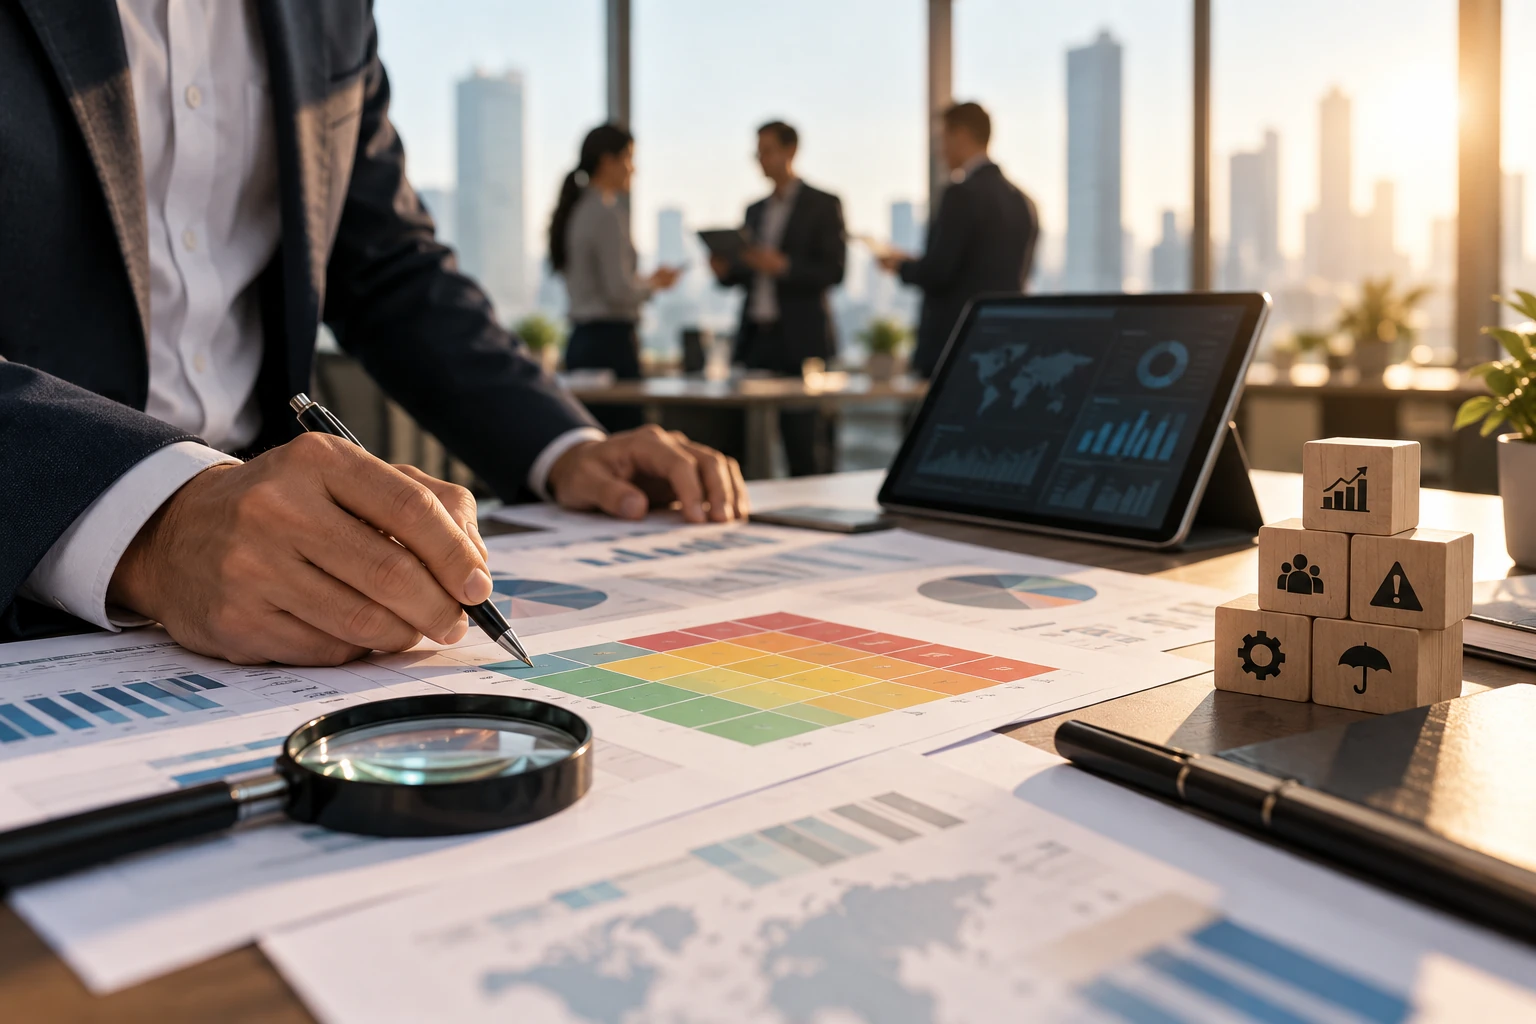
    Business Risk Assessment

    What Our Business Risk Assessment Reviews

    Our review connects the risks in your business with the checks used to manage them.

    1. Customers, Services and Transactions

    We begin with who you serve and how money moves through your business. Customer ownership, payment routes, transaction volumes, geographic links, and access to your services all help explain the exposure. We also discuss unusual patterns with your team. A change in activity may have a reasonable explanation, but it needs to be understood before a risk rating is assigned.

    2. How Your AML Controls Work

    A procedure can be clear on paper and still be difficult to follow during a busy working day. We examine customer checks, screening, transaction monitoring, escalation, and management oversight. Supporting records help us see whether these controls are being applied consistently. Where audit findings or unresolved issues point to a weakness, we consider what that means for the assessment.

    3. Risks That Need Further Action

    Once the controls have been reviewed, we assess the exposure left behind. We help you compare it with your organisation’s risk appetite and identify where further safeguards are needed. The recommendations explain what should change and why. This gives management a way to prioritise the work rather than treating every finding as equally urgent.

    Our Approach

    We work with your team to understand the evidence, assess the risks, and plan the next steps.

    1
    Establish the Starting Point

    First, we agree on the scope and the period being assessed. We discuss your operations, review the available information, and identify the people who can explain it. If records are missing or inconsistent, we flag that before relying on them.

    2
    Assess the Business Risks

    We examine the exposure associated with your customers, services, markets, transactions, and delivery channels. This stage considers risk before existing controls are applied. We explain the method used and record the reasoning behind the ratings, including assumptions that could affect the results.

    3
    Examine the Controls

    We review the safeguards relevant to each risk and look for evidence of their use. A control’s effectiveness depends on more than its presence in a policy. We consider how it operates, where it falls short, and what exposure remains as a result.

    4
    Turn Findings Into Decisions

    We document the results and help your team put the recommended improvements in order. Some findings may call for a policy update; others may need a stronger check or clearer responsibility. We also discuss the changes that should trigger a review of the assessment.

    Who Needs Business Risk Assessment Support?

    Exchange Houses
    Banks and Financial Institutions
    Designated Non-Financial Businesses and Professions
    Organisations Reviewing Their AML Framework

    Ideal for businesses completing their first assessment, revisiting earlier findings, or reviewing how changes in operations affect their AML exposure.

    Why Choose Vertex Compliance?

    Shaped by Your Operations

    We ask how your business works before deciding how to assess it. An exchange house handling remittances has different exposure from a property business. Your activities, customer relationships, and payment routes provide the starting point for our work.

    Clear Reasoning

    Management needs to understand the ratings it is asked to act on. We explain the evidence behind our conclusions and identify where information is limited. This makes it easier to discuss the findings and question assumptions before decisions are made.

    Focused Recommendations

    A recommendation should address a specific weakness. We explain the connection between the finding, the risk it creates, and the proposed change. Your team can then judge the priority and decide how to carry out the work.

    Findings Inform Policies

    Risk findings should influence the way your business manages AML exposure. We help you identify where policies, procedures, or safeguards need updating, so the assessment becomes a reference for operational decisions rather than a report that is filed away.

    Meet the Experts

    Sarah Khan
    Vasantha Madan Mohan

    Managing Director
    Sarah Khan
    Sridhar Rajam

    Associate Partner

    Sarah Khan
    Arjun Mohan

    Director – Sales & Marketing
    Frequently Asked Questions

    It helps answer two questions: where could your business be exposed to money laundering or terrorist financing, and how well are you managing that exposure? The review brings together your business activity and control findings, then identifies areas that need further attention.
    Yes, although the two are connected. Customer assessments look at individual relationships. The business assessment considers the combined exposure across your customer base, services, markets, and transaction activity. It helps you judge whether the controls used across the organisation are appropriate.
    We can begin by identifying what is available and what is missing. Some gaps may need to be resolved before reliable ratings can be reached. Where information remains limited, the assessment should make that limitation clear rather than present an unsupported conclusion.
    It means the risk left after your controls are considered. For example, checking a customer’s ownership can reduce exposure, but only if the information is reliable and unresolved questions are followed up. The assessment considers how well that check works when judging the remaining risk.
    Review it at the intervals appropriate to your business and regulatory obligations. Significant changes may also require an earlier update. Entering a new market, introducing a service, or finding a serious control weakness can affect conclusions reached in the previous assessment.
    Start with the priorities. Assign each agreed action to someone who can carry it through, set a realistic deadline, and track completion. Where findings affect existing policies or checks, update them. Follow-up should establish whether the weakness has been addressed.