Call us today +971 - 56411 3575 or +971 - 58914 9282 | Email: info@vertexcompliance.com

ML/TF Risk Assessment

Pinpoint your highest-priority ML/TF risks and take action where it matters most.

Request an Assessment

    About ML/TF Risk Assessment

    Every business has a different risk profile. The customers you work with, the countries you deal with, the type of services you offer and the way money moves through your business can all affect your exposure to money laundering and terrorist financing.

    An ML/TF risk assessment looks at those areas in detail. It helps you understand which parts of the business carry more risk and whether the controls already in place are enough to manage it.
    At Vertex Compliance, we tailor the assessment to your actual operations.

    We examine the daily operations of the business, not just the written policies. After completing the review, you will receive documented risk ratings, explanations for them, and a clearer understanding of where action may be necessary.
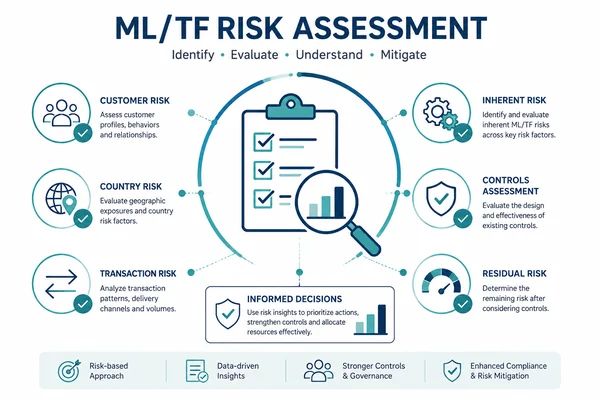
    ml ft risk assessment

    What Our ML/TF Risk Assessment Reviews

    The assessment looks at the areas that can change your overall exposure to ML/TF risk.

    1. Business Activities, Products and Channels

    DNFBPs require a documented view of the risks associated with their clients, business activities, and service delivery methods. This includes the products you offer, the types of transactions involved and whether customers deal with you directly, online or through another party. Some activities naturally create more exposure than others. High-value transactions, complex ownership structures, digital onboarding or the use of intermediaries can all change the level of risk. We also look at payment methods and delivery channels to understand where additional checks or controls may be needed.

    2. Customers, Countries and Transactions

    Not every customer carries the same level of risk. We look at the types of customers you deal with, what they do, where they are based and how they normally use your services. We also consider geographic exposure, including the countries connected to your customers, transactions or business relationships, particularly where higher-risk jurisdictions are involved. Transaction behaviour is another important part of the assessment. We look at values, frequency, patterns and other factors that may affect the overall risk level.

    3. Existing Controls and Remaining Risk

    Once we identify the primary risks, we look at what your business already does to control them. This may include customer due diligence, enhanced checks, screening, transaction monitoring, internal approvals, reporting and staff training. The next question is simple: after those controls are taken into account, how much risk is still left? That remaining exposure is documented so your team can see which areas are under control and which ones may need more attention.

    Our Approach

    We keep our assessment focused, practical and relevant to your business.

    1
    Understand Your Business

    We start by getting a proper picture of how your business operates. That includes your customers, services, locations, transaction activity, payment routes and delivery channels. We also agree on the scope before the assessment begins, so everyone is clear about what will be covered.

    2
    Look at the Risk Factors

    Next, we go through the information that affects your ML/TF exposure. This may include customer data, geographic links, transaction patterns, product risks and the controls already being used. Where something is not clear from the documents, we may speak with the people who handle the process in practice.

    3
    Rate the Risk

    We then consider each relevant risk area and rate them. We look at the level of exposure before controls are applied and then at the risk that remains after those controls are taken into account. We record the reasoning behind the rating, so the result is not just a number sitting in a spreadsheet with no explanation.

    4
    Set Out the Next Steps

    At the end of the assessment, you receive a documented view of the main ML/TF risks across the business. Where further action is needed, the recommendations are set out in order of priority. This makes it easier to decide what should be dealt with first rather than trying to fix everything at once.

    Who Is an ML/TF Risk Assessment For?

    Banks and Financial Institutions
    Designated Non-Financial Businesses and Professions
    Virtual Asset Service Providers
    Payment and Remittance Businesses

    Ideal for UAE-regulated businesses that need to identify, assess, and prioritise their money laundering and terrorist financing risks.

    Why Choose Vertex Compliance?

    Tailored Assessment

    Your ML/TF risks depend on your customers, services, transactions, delivery channels, and geographic exposure. We assess these factors in the context of your business instead of relying on broad assumptions.

    Clear Risk Ratings

    A risk rating is only useful when your team understands how it was reached. We document the factors considered and explain the reasoning behind each assigned rating.

    Prioritised Actions

    Identifying a risk is not enough—your team must also know what to address first. We provide practical recommendations based on urgency and potential impact.

    Defensible Findings

    Management, auditors, or regulators may ask how your business assessed its ML/TF risks. We clearly document the methodology, findings, and conclusions so your approach can be explained with confidence.

    Meet the Experts

    Sarah Khan
    Vasantha Madan Mohan

    Managing Director
    Sarah Khan
    Sridhar Rajam

    Associate Partner

    Sarah Khan
    Arjun Mohan

    Director – Sales & Marketing
    Frequently Asked Questions

    It is a review of the factors that could expose your business to money laundering or terrorist financing. This may include customers, products, services, countries, transactions and the way customers access your business.
    There is no single timeline for every business. It depends on the size of the organisation, the scope of the review, the number of activities involved and how quickly the required information is available.
    That depends on the business. We may need customer information, product details, transaction data, geographic information, current risk assessments and details of the controls already in place.
    Yes. We look at the risk before controls are considered and then at the level of risk that remains after those controls are applied.
    You receive a documented assessment showing the main ML/TF risks, the risk ratings, the reasons behind those ratings and any areas that may need further attention.
    Yes. If the assessment highlights areas that need work, Vertex Compliance can support remediation, documentation, policy changes and improvements to existing controls.