Call us today +971 - 56411 3575 or +971 - 58914 9282 | Email: info@vertexcompliance.com

Fintech Compliance Solutions: 8 Controls to Review Before Scaling

Fintech Compliance Solutions: 8 Controls to Review Before Scaling

Your payment app is gaining customers. A distribution partner wants to bring in more users. The product team has a feature ready, and investors are asking when you will enter the next market.

Then someone asks whether the onboarding process can handle twice as many applications.

Nobody has tested it.

Growth has a way of exposing problems that were easier to manage with fewer customers. Manual checks become backlogs. Payment differences take longer to investigate. Employees start making exceptions because the existing process cannot keep up.

Fintech compliance solutions should help you identify these weaknesses before expansion adds pressure. The starting point is a practical review of how your business operates today and what will change when it grows.

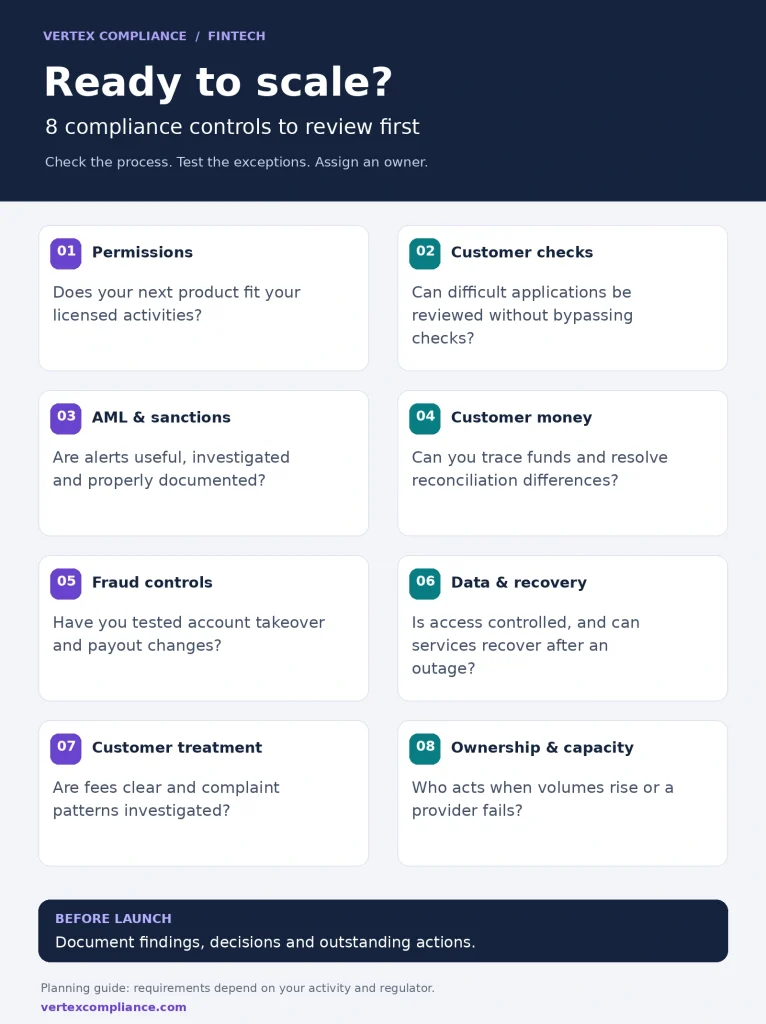
Controls to Review before Scaling

A digital wallet, payment gateway and lending platform do not have identical compliance needs. Your controls should reflect your activities, customers, payment flows and regulatory obligations.

For a UAE fintech, begin by confirming the requirements that apply to its licence and regulator. Then review customer onboarding, financial crime controls, customer money, technology and consumer protection.

Bring product, operations, finance and compliance into the discussion. Each team sees different problems. A customer complaint might reveal a settlement issue that never appears in a compliance report.

Use the following checks to guide that conversation.

1. Confirm Your Permissions Before Expanding

A new feature can change your regulatory position.

Perhaps your platform currently connects buyers and sellers but will soon hold customer balances. Or you process domestic payments and want to introduce overseas transfers.

Have the proposed activity assessed before committing to a launch date. The CBUAE’s retail payment framework distinguishes between different services, so calling a product a “payments app” does not establish which permissions it needs. rulebook.centralbank.ae

Write down who receives funds, who holds them and who executes transactions. Include every partner involved.

Do not assume a partner’s licence automatically permits your own activities. Get clarity on each business’s responsibilities and any approvals required for the proposed arrangement.

2. Review KYC and Customer Onboarding

Most onboarding demonstrations show a customer with clear documents and straightforward information.

Actual applications are messier.

Names differ between records. An identity check fails. A business customer has several ownership layers. Someone submits another application after being rejected.

Follow a sample of difficult cases through your Know Your Customer process. Can reviewers see why a check failed? Can they request more information? Is the reason for approving an exception recorded?

Check what incomplete applications allow customers to do. Any access before outstanding checks are resolved needs to be permitted and appropriately restricted.

Also measure the queue. If applications already wait several days for manual review, a marketing campaign could turn a manageable delay into a serious backlog.

3. Review AML Monitoring and Sanctions Screening

A monitoring rule can be switched on without producing useful results.

A rule focused on individual large transfers, for example, may miss suspicious activity involving several smaller payments. Another might produce so many alerts that investigators struggle to identify urgent cases.

Review AML monitoring against your products, customer groups and payment routes. Ask whether the information investigators receive is sufficient to understand an alert.

Sanctions screening needs attention when relevant lists, customer details or connected parties change.

Check what happens after a potential match. Who investigates? Who can stop activity? What evidence supports the decision?

The CBUAE’s payments guidance discusses financial crime risks associated with payment products and services. Use those risks to challenge whether your controls fit your actual business. rulebook.centralbank.ae

4. Trace Customer Funds and Reconciliations

Pick a payment and follow it from receipt to settlement.

Then try a refund, a failed transaction and a payment received near the daily reporting cut-off. Can finance and operations explain where the money is at each stage?

Where safeguarding requirements apply, check that your arrangements meet the rules for your activity.

Reconciliation deserves particular attention. Who investigates differences between customer balances and underlying records? How are unresolved amounts tracked? Who takes over when the usual employee is absent?

Avoid accepting “the system handles it” as a complete answer. Ask someone to demonstrate the process and explain a recent mismatch.

Higher transaction volumes will make unexplained differences harder to investigate.

5. Test Your Fintech Fraud Controls

Fraud prevention needs its own review alongside AML compliance.

Consider account takeover, stolen credentials, fake merchants, refund abuse and changes to payout details.

Test realistic scenarios in a controlled environment. What happens when a customer resets a password and immediately changes their bank account? Can repeated failed payment attempts continue without review?

Check employee permissions too. Support staff need enough access to resolve problems, but sensitive actions should have appropriate restrictions and records.

Review legitimate customers affected by fraud controls. If people are repeatedly blocked without a clear reason, complaints will rise—and staff may begin finding ways around the process.

Investigate both missed fraud and unnecessary restrictions.

6. Review Data Security and Business Continuity

Start with access to customer information.

Who can view identity documents, payment records and support conversations? Include contractors, service providers and employees who have changed roles.

Check whether access is removed promptly and whether sensitive actions can be traced.

Then test a service disruption. If your screening provider becomes unavailable, does onboarding pause, queue applications or follow an approved contingency process?

Someone needs authority to choose the response.

Ask for evidence that backups can be restored. A successful backup notification does not prove your team can recover the service and its records.

Check that recovery plans reflect dependencies between systems, rather than treating each supplier separately.

7. Check Consumer Protection and Complaints

Read the customer journey on a phone.

Are fees visible before confirmation? Are payment limits understandable? Does the refund explanation match what happens in practice?

Pay attention to messages shown when something goes wrong. “Transaction unsuccessful” gives customers little help if money has left their account.

Complaints can expose problems before management reports do. Several customers describing delayed refunds may point to a broken handoff between support and finance.

Assign someone to investigate recurring issues and report findings to product and operations.

Customers reporting suspected fraud also need a clear route to help. They should not have to contact several departments while an account remains exposed.

8. Assign Owners and Check Team Capacity

A control needs someone who can act when it identifies a problem.

Name the owner, the person authorised to approve changes and the backup contact.

Then look at workload. If alerts double, how many additional reviews can your team realistically complete? If a provider misses a deadline, who follows up?

Before launch, agree which findings must be resolved and which can be managed through documented restrictions.

Track overdue actions, unresolved cases and repeated errors. These show where work is getting stuck.

A policy update may be complete while the process it describes remains broken. Check what employees actually do before marking an issue closed.
Review Your Fintech Compliance Solutions with Vertex Compliance

Before scaling, your team should be able to explain its main risks, demonstrate its controls and identify who handles exceptions.

If those answers are unclear, resolve the gaps while changes are still manageable. Waiting until customer numbers rise usually means more records to review and more people affected.

Vertex Compliance’s fintech compliance solutions draw on its advisory services for fintech setup, policy drafting, anti-fraud frameworks, data protection and consumer protection. 

Discuss Your Fintech Compliance Needs to identify support relevant to your UAE business, its activities and expansion plans.

FAQs

1. When should a fintech review its compliance controls?

Before launching a product, entering a market or significantly increasing transaction capacity. Repeated complaints, incidents and growing review backlogs are also reasons to reassess existing controls.

2. Does compliance software make a fintech compliant?

Software supports checks and monitoring. Your team still needs to configure it correctly, investigate exceptions and assess whether its results remain useful as products and customers change.

3. Which compliance controls should we review first?

Confirm that proposed activities fit your permissions. Then prioritise weaknesses affecting customer funds, financial crime prevention and service continuity, based on the risks of your planned expansion.

4. Can a fintech outsource compliance tasks?

Some tasks may be outsourced where permitted. Check applicable conditions, retain oversight and agree how the provider will escalate concerns, protect information and demonstrate completed work.

5. What records should a compliance review produce?

Keep the scope, test results, findings and corrective actions. Record decisions about outstanding risks, who approved them, any temporary restrictions and when those decisions must be reviewed.
How to Conduct an AML Gap Assessment in the UAE

How to Conduct an AML Gap Assessment in the UAE

An AML policy may look complete on paper and still fail when someone tries to use it.

Perhaps the customer risk rating does not match the information in the file. A sanctions alert was cleared, but nobody recorded why. An employee noticed an unusual payment but did not know whom to tell. These are the gaps that create real compliance problems.

An AML gap assessment in the UAE helps you find those weaknesses before a regulator, auditor or criminal does. It compares what your business should be doing with what happens in practice. More importantly, it gives you a sensible plan for fixing what is missing.

Here is how to conduct an assessment that produces useful answers, not another report that sits unopened in a folder.

What Is an AML Gap Assessment?

An AML gap assessment is a structured review of your anti-money laundering and counter-terrorist financing controls.

It looks at your policies, customer files, risk assessments, screening, transaction monitoring, reporting, training and record-keeping. Each area is checked against the legal and regulatory requirements that apply to your business.

The objective is simple: identify the difference between your current AML programme and the standard you need to meet.

This is not the same as checking whether a policy exists. A policy might say that high-risk customers receive enhanced due diligence, but do your files contain evidence of those checks? Are approvals documented? Is the source of funds understood? A proper AML/CFT gap assessment tests those details.

Why This Matters Now

Financial crime methods are changing quickly. Criminal networks use shell companies, trade payments, informal value-transfer systems, virtual assets and third-party accounts to make transactions look legitimate.

A 2026 report by the Financial Action Task Force states that more than GBP 130 million in cash was transported to the UAE within three months and declared as gold-trading funds. The case shows why businesses must question unusual cash movements, cross-border payments and transactions that do not fit the customer’s stated activity. FATF 2026 report

UAE businesses cannot rely on generic controls or an old compliance manual. They need controls that reflect their customers, products, payment routes and actual exposure.

Steps to Conduct an AML Gap Assessment in the UAE

Start With Your Scope

Before opening customer files, decide what the assessment will examine.

Start with the legal entities, branches, departments and regulated activities included in the review. Then identify the regulators and AML requirements that apply. A financial institution may have different obligations from a real estate broker, auditor, company service provider or dealer in precious metals and stones.

Your scope should normally include:

  • Business-wide AML risk assessment
  • AML/CFT policies and procedures
  • Customer due diligence and enhanced due diligence
  • Beneficial ownership checks
  • Sanctions and politically exposed person screening
  • Transaction monitoring
  • Suspicious transaction escalation and reporting
  • Employee training
  • Governance, oversight and record-keeping

Keep the scope realistic. If you try to review everything without enough time or evidence, you will end up with shallow findings.

Review Your AML Risk Assessment

Your business-wide risk assessment should explain where your exposure comes from. It should consider customers, countries, products, services, delivery channels and transaction patterns.

Do not accept broad statements such as “the company has a medium money-laundering risk.” Ask how that conclusion was reached.

Check whether the assessment reflects the business as it operates today. Has the company entered new markets? Does it now accept cash, virtual assets or overseas payments? Has it started working with intermediaries? Has the customer base changed?

Look at the scoring method as well. The factors, weightings and final ratings should make sense. If every customer ends up with a medium rating, the model is probably not distinguishing risk properly.

An effective AML risk assessment in the UAE should lead to stronger controls for higher-risk areas. If the assessment has no effect on due diligence, monitoring or approval decisions, it is not doing its job.

Compare Policies With Practice

Now compare the written AML framework with what employees actually do.

Select a sample of customer files and follow each process from beginning to end. Check how the customer was identified, screened, risk-rated, approved and monitored. Speak with the people performing these checks. Their answers often reveal gaps that documents do not show.

For example, a procedure may require independent verification of changed bank details. In practice, the employee may confirm the change by replying to the same email that requested it. The policy exists, but the control is weak.

Record both design gaps and operating gaps. A design gap means the required control is missing or poorly written. An operating gap means the control looks adequate but is not being followed consistently.

Test Customer Due Diligence

Customer due diligence is one of the most important parts of an AML compliance review in the UAE.

Review a balanced sample of low-, medium- and high-risk customers. Include recent files, older relationships and customers from higher-risk sectors or locations.

For each file, ask:

  • Is the customer’s identity properly verified?
  • Is the beneficial owner identified and supported by reliable evidence?
  • Is the purpose of the relationship clear?
  • Does the expected activity match the customer’s profile?
  • Were sanctions and PEP checks completed?
  • Were high-risk relationships approved at the correct level?
  • Is enhanced due diligence recorded where required?
  • Has the information been reviewed and updated?

Do not focus only on missing documents. A file can contain plenty of documents without explaining who controls the company, where its money comes from or why it is making certain payments.

Examine Screening and Monitoring

Next, look at how the business identifies sanctions exposure, PEPs, adverse information and unusual transactions.

Check when screening happens. It should not be limited to customer onboarding. Relevant parties need to be screened when information changes and against updated lists, according to the organisation’s obligations and risk exposure.

Review how alerts are handled. Who investigates them? What information is considered? Can management see why an alert was closed?

Then test suspicious transaction monitoring. Look at whether the rules reflect the business’s genuine risks. Warning signs may include sudden changes in payment behaviour, unnecessary third-party transfers, repeated transactions just below internal limits or payments involving countries unrelated to the customer’s business.

A large number of alerts does not prove that monitoring is effective. If employees close them without proper investigation, the system creates activity rather than protection.

Review STR Reporting

Employees should know how to raise a concern internally and when it must reach the compliance officer or MLRO.

Review internal escalation records and a sample of investigated cases. Check whether concerns were handled promptly, decisions were documented and supporting evidence was retained.

Where a suspicion meets the reporting requirement, the appropriate report must be submitted to the UAE Financial Intelligence Unit through goAML. The reporting process should also protect confidentiality and prevent tipping off.

An STR reporting UAE review should ask a difficult question: were any cases closed because the business lacked information rather than because the activity was genuinely reasonable?

Silence is not evidence that there are no suspicious transactions. It may mean employees are not recognising or escalating them.

Check Governance and Training

AML compliance cannot sit entirely with one compliance employee.

Senior management should understand the organisation’s main financial-crime risks, receive meaningful reports and make informed decisions about serious issues. Responsibilities should be clear, especially for approving high-risk customers, resolving overdue reviews and closing remediation actions.

Training also needs closer attention. A yearly presentation is rarely enough. Employees should understand the warning signs connected to their own work.

Finance teams may need training on unusual payment instructions. Sales teams should understand customer onboarding risks. Senior managers need to know what they are approving and why.

Test understanding through interviews, scenarios or short knowledge checks. Attendance records alone will not tell you whether the training worked.

Rank the Gaps

Once the testing is complete, do not give management a long list in which every issue appears urgent.

Rate each gap according to regulatory impact, financial-crime exposure, likelihood, customer harm and reputational consequences. Distinguish critical failures from documentation improvements.

Each finding should explain:

  • What is wrong
  • Why it matters
  • What evidence supports the finding
  • What needs to change
  • Who should own the action
  • When it should be completed

A practical remediation plan is the most valuable output of an AML gap assessment. Without named owners and deadlines, findings tend to remain open.

Avoid Common Assessment Mistakes

One common mistake is reviewing documents without testing customer files. Another is copying a checklist designed for a different industry.

Businesses also weaken the process by interviewing only compliance staff. Operations, finance, sales, onboarding and senior management may see entirely different parts of the same risk.

Finally, do not hide uncomfortable findings. The purpose of the review is not to prove that the programme is perfect. It is to find problems while they can still be corrected.

When Should You Conduct a Review?

An AML gap assessment should be completed periodically and whenever the business changes significantly.

Consider a review after entering a new market, launching a product, changing ownership, adopting a new monitoring system or receiving regulatory feedback. It is also sensible before an inspection or independent audit—but not the week before it begins.

Allow enough time to examine evidence, speak with employees and fix serious weaknesses.

Turn the Findings Into Action

A strong AML gap assessment gives management an honest view of the organisation’s position. It shows which controls work, where exposure remains and what should happen next.

The assessment should leave you with more than a compliance score. You should receive clear findings, sensible priorities, responsible owners and a realistic remediation plan.

Vertex Compliance helps UAE businesses review their AML/CFT frameworks, test how controls operate and address weaknesses before they grow into regulatory problems. If you are unsure whether your current controls would stand up to scrutiny, an independent assessment is a practical place to start.

Frequently Asked Questions

1. How can we tell if our AML controls have gaps?

Some gaps are easy to spot, such as missing customer documents or overdue reviews. Others only appear when you test the process properly. If employees handle the same situation differently, alerts are closed without clear reasons or high-risk customers receive no extra checks, your AML controls need a closer review.

2. Who needs an AML gap assessment in the UAE?

Financial institutions and DNFBPs can benefit from an assessment. This includes real estate businesses, auditors, accountants, company service providers and dealers in precious metals and stones. It is particularly useful before a regulatory inspection or after a major business change.

3. When should we review our AML controls?

Do not wait until an inspection is announced. Review your controls when the business changes. For example, when you start serving a new market, offer a new service or take on customers with a different risk profile. It is also worth doing if your last review was some time ago or the same compliance issues keep returning.

4. How much time should we set aside?

That depends on what needs to be checked. A smaller business with organised records may need only a few weeks. It will take longer if there are several branches, large numbers of customer files or missing information. Rushing the review usually means important gaps get overlooked.

5. What do we receive at the end?

You receive a clear account of what is working, what is missing and what needs attention first. It should also tell you who needs to handle each action and give your team workable deadlines, not leave you with a technical report that nobody knows how to use.